Engineer resilient defenses
Design layered controls, segmented environments, and dependable telemetry that reduce risk across infrastructure, endpoints, networks, applications, and cloud platforms.
BTL1- and SAL1-certified SOC analyst with 10 years in IT and about two years of hands-on SOC lab work. I investigate alerts, build detections in Splunk and Wazuh, and automate response with n8n.
Design layered controls, segmented environments, and dependable telemetry that reduce risk across infrastructure, endpoints, networks, applications, and cloud platforms.
Triage alerts, validate threats and vulnerabilities, and turn technical evidence into prioritized remediation.
Automate enrichment and response workflows, improve playbooks, and turn lab lessons into stronger detections.
Technical capability
Hands-on experience across monitoring, investigation, testing, automation, infrastructure, and security frameworks.
SOC workflows, alert triage, incident classification, false-positive reduction, IOC correlation, Cyber Kill Chain analysis, and MITRE ATT&CK mapping.
Packet analysis, IDS/IPS rule authoring, wireless assessment, MITM detection, and investigation of suspicious network activity.
Controlled wireless reconnaissance, monitor-mode workflows, handshake capture, WPS testing, evil-twin simulation, and password-audit labs.
Endpoint monitoring, forensic collection, disk and memory analysis, malware triage, response playbooks, and evidence preservation.
OWASP-aligned web, API, and Android testing across authorization, authentication, injection, transport, storage, and client-side controls.
Passive and active discovery for target profiling, subdomain enumeration, DNS analysis, and attack-surface mapping.
Security scripts, log parsing, IOC detection, API integrations, alert enrichment, ticketing pipelines, and repeatable analyst workflows.
Static and dynamic application builds, REST API development, front-end interactions, backend services, test automation, and deployment support.
AWS security reviews, IAM and S3 misconfiguration analysis, CloudTrail review, risk assessment, policies, and framework-based gap analysis.
Controlled Windows and Active Directory exercises, privilege escalation, post-exploitation, and detection validation in authorized labs.
Selected evidence
Every project below is published on GitHub and includes the full lab report with readable technical evidence.
 01 / 12
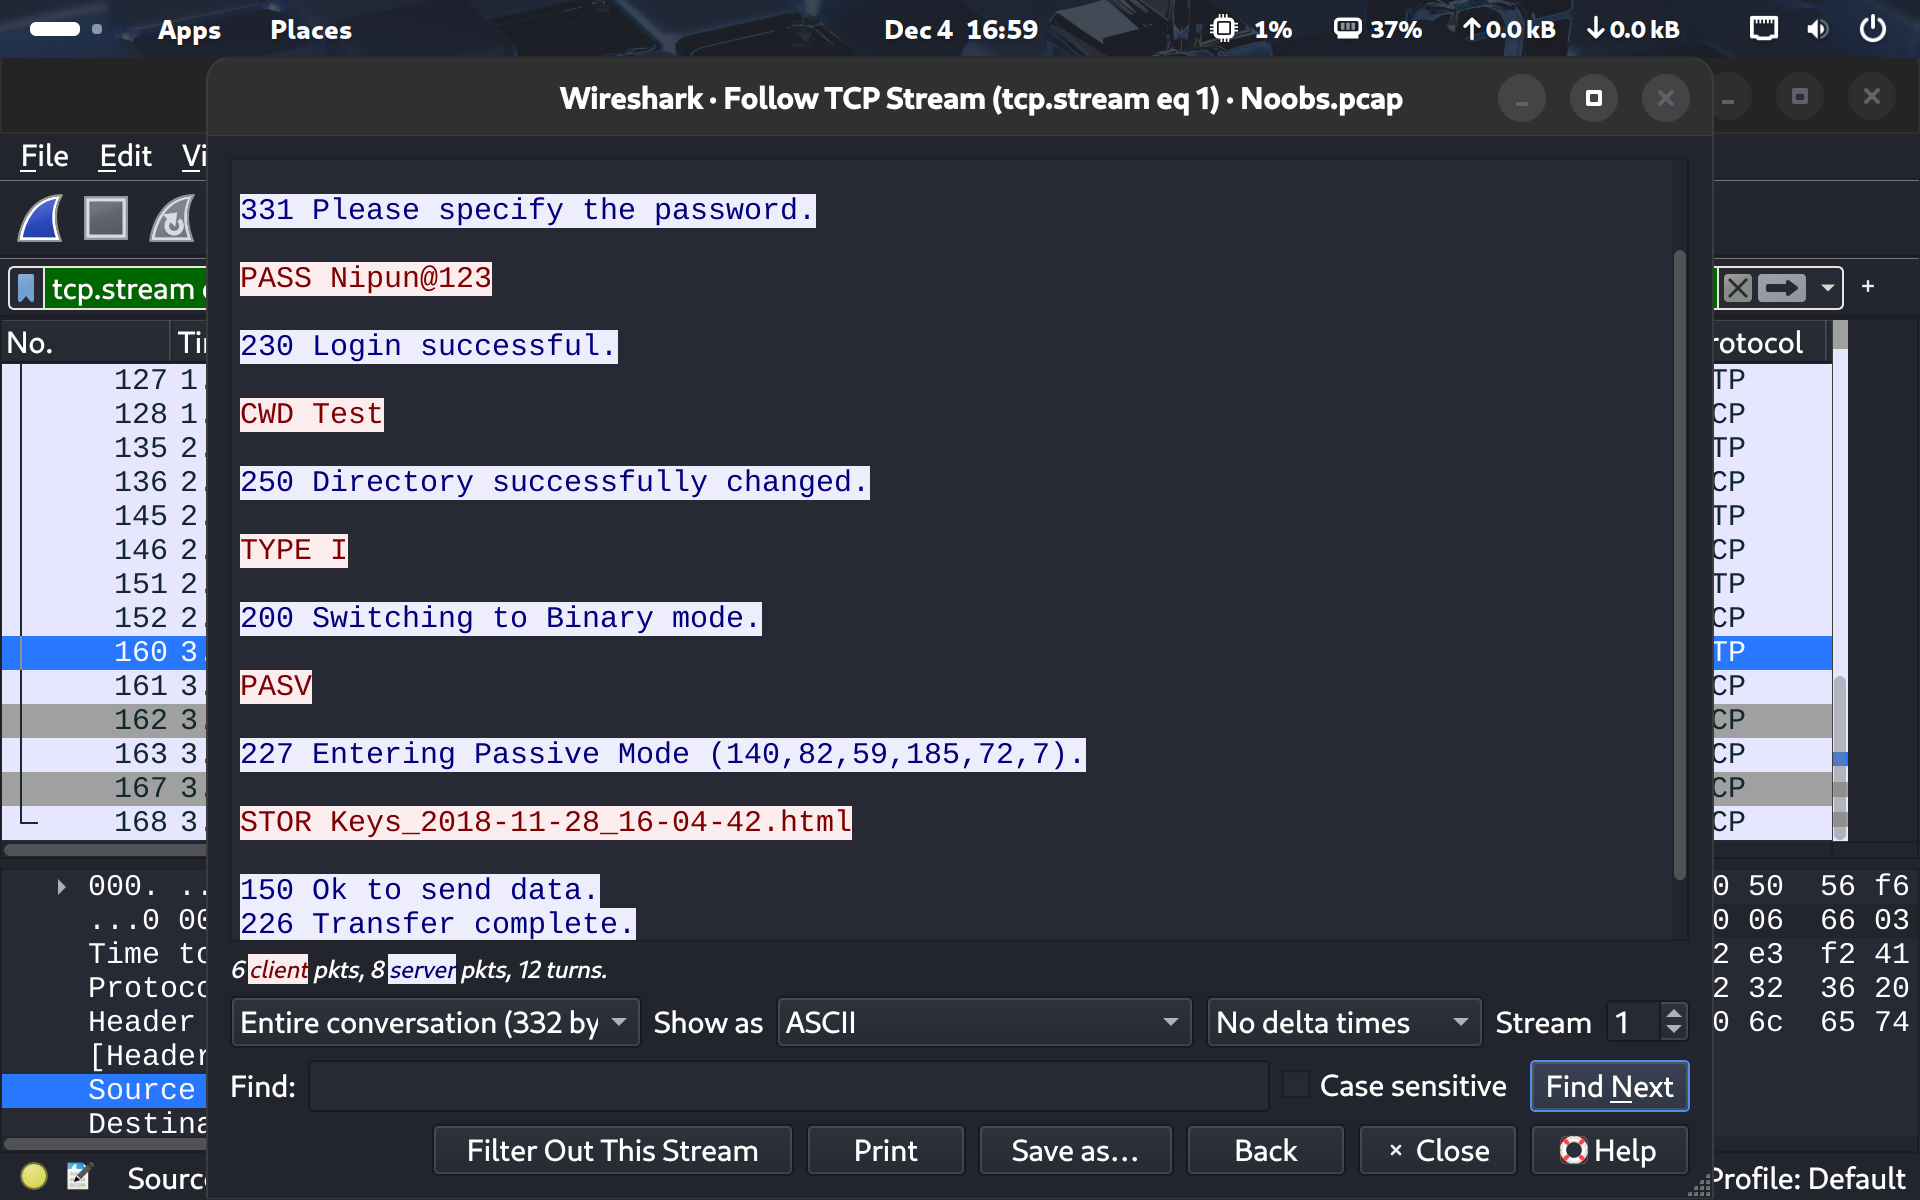
Network Security · 9 evidence images
Investigated keylogger exfiltration in packet traffic and created Snort rules for ICMP and Nmap SYN-scan detection.
View detailed case study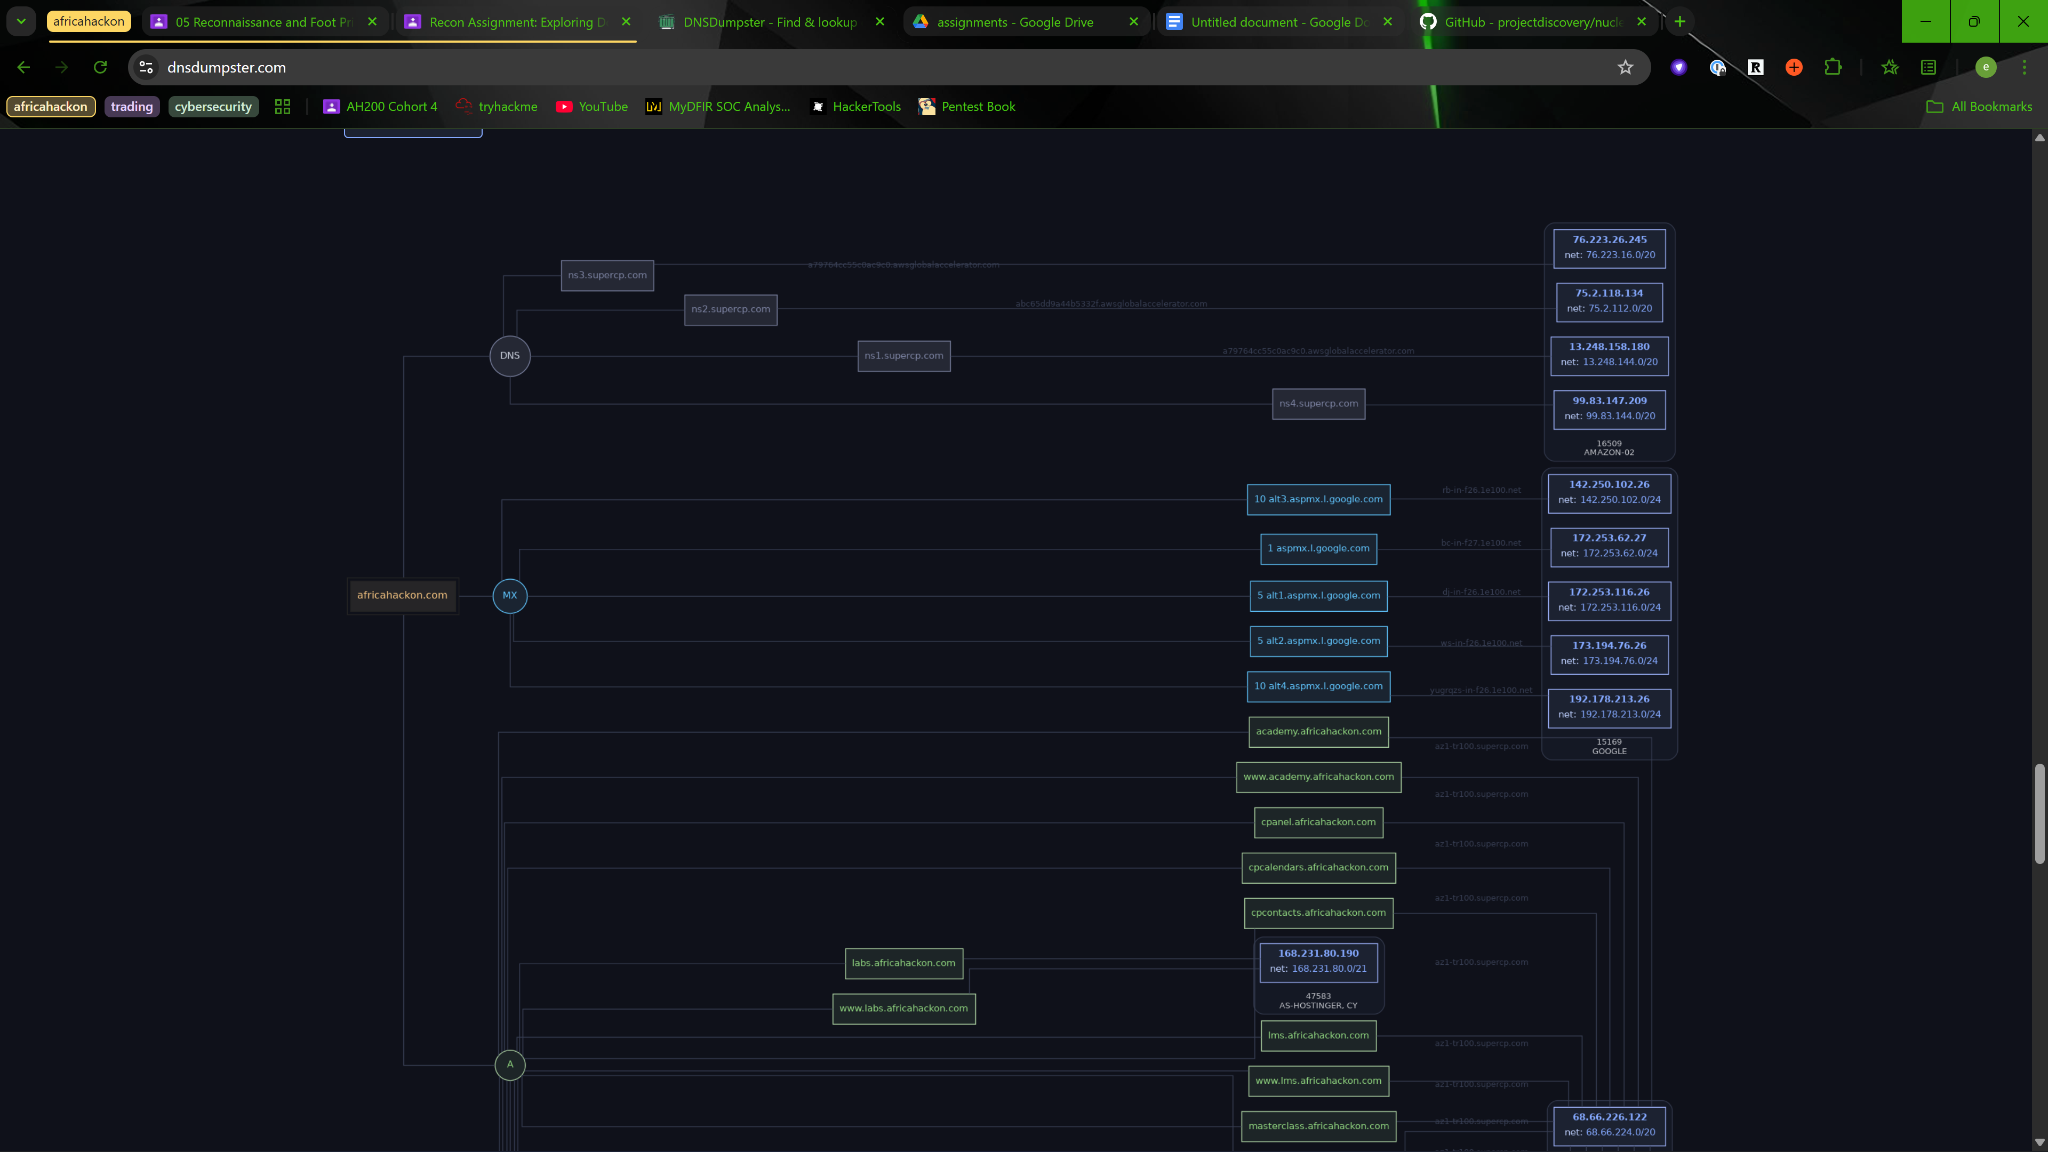 02 / 12
Reconnaissance · 7 evidence images
Used multiple passive and active reconnaissance methods to enumerate subdomains, distinguish live from inactive assets, and inspect perimeter protections.
View detailed case study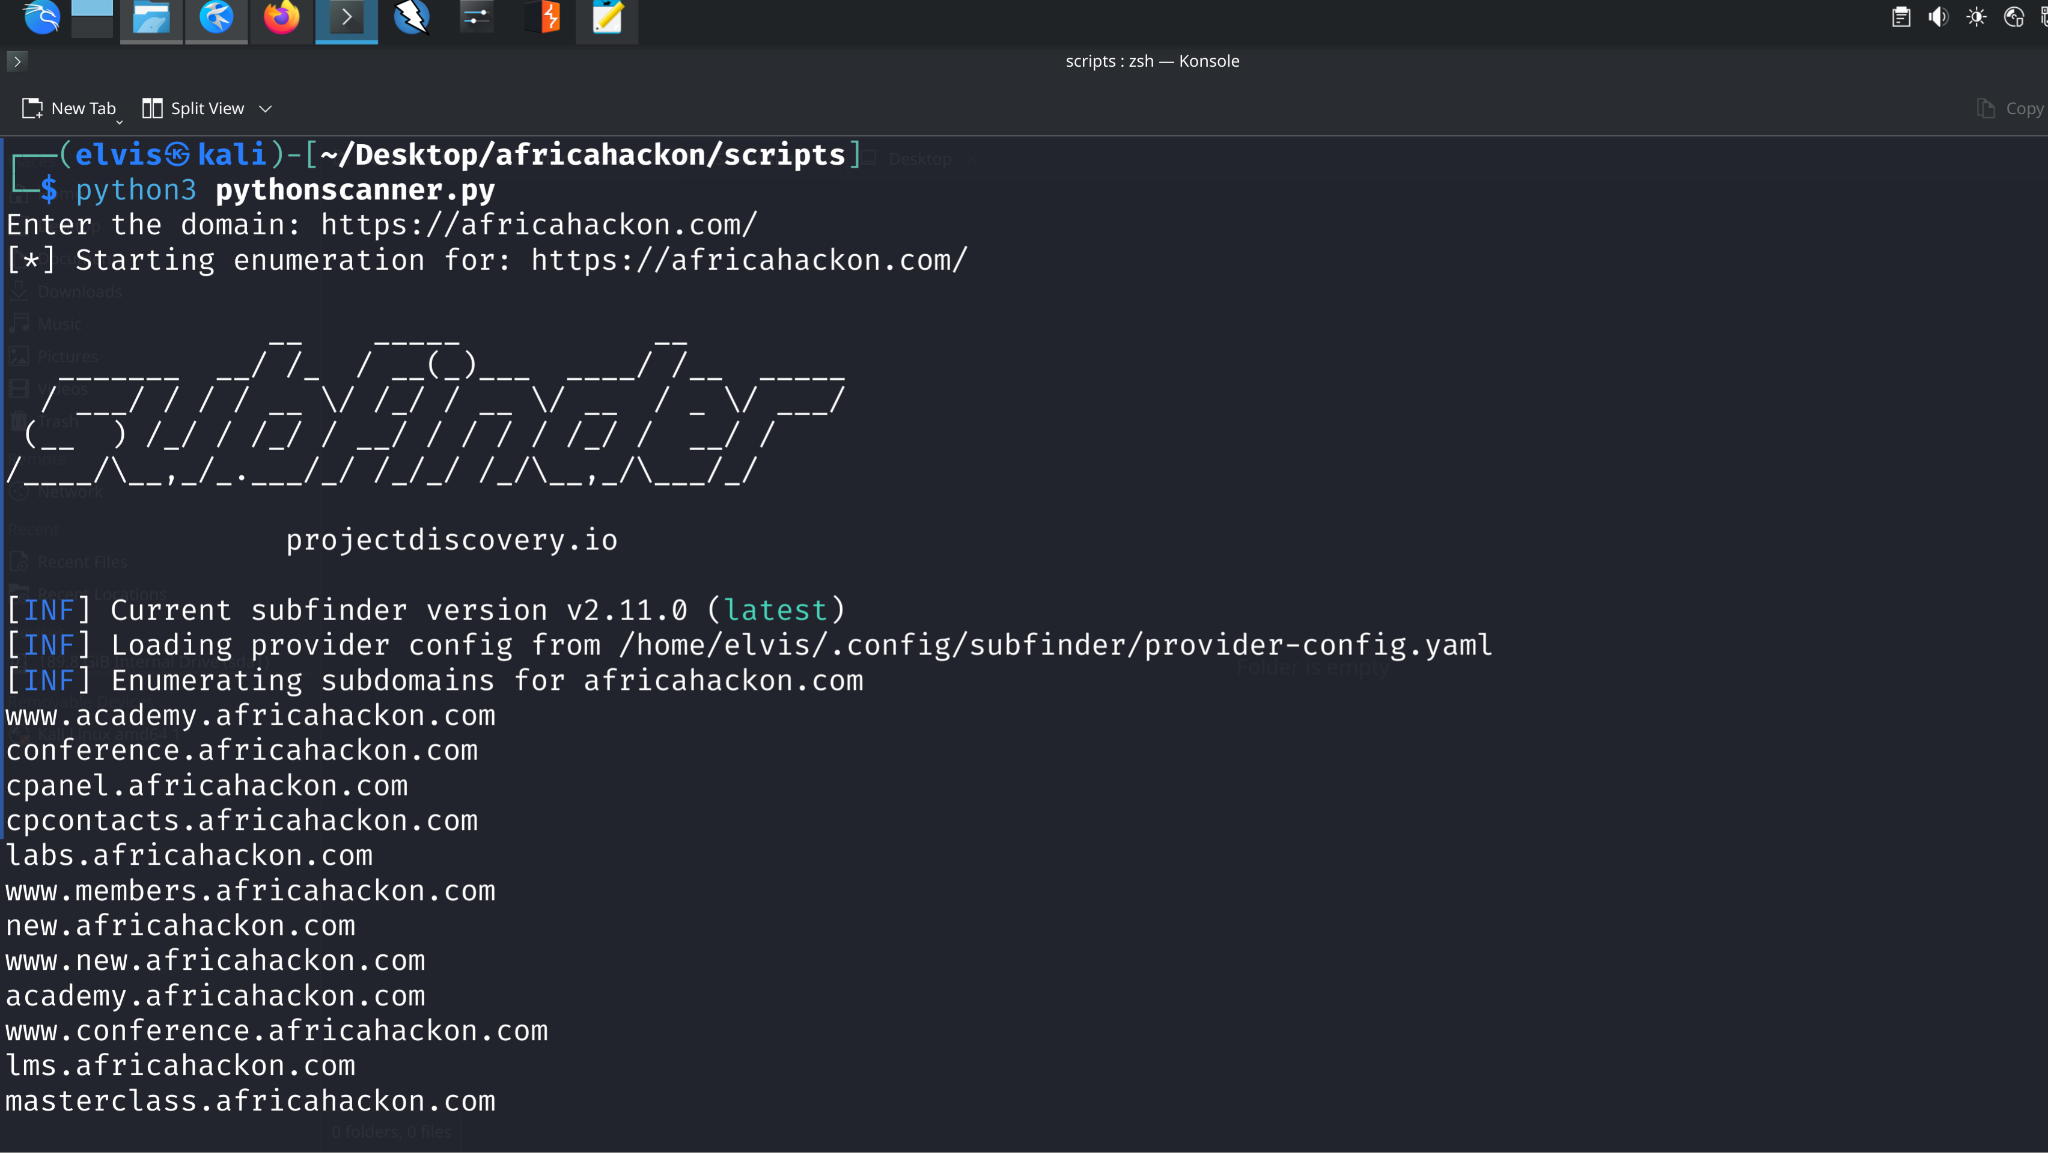 03 / 12
Scripting · 3 evidence images
Automated subdomain discovery and live-host probing by orchestrating Subfinder and httpx from a reusable Python command-line workflow.
View detailed case study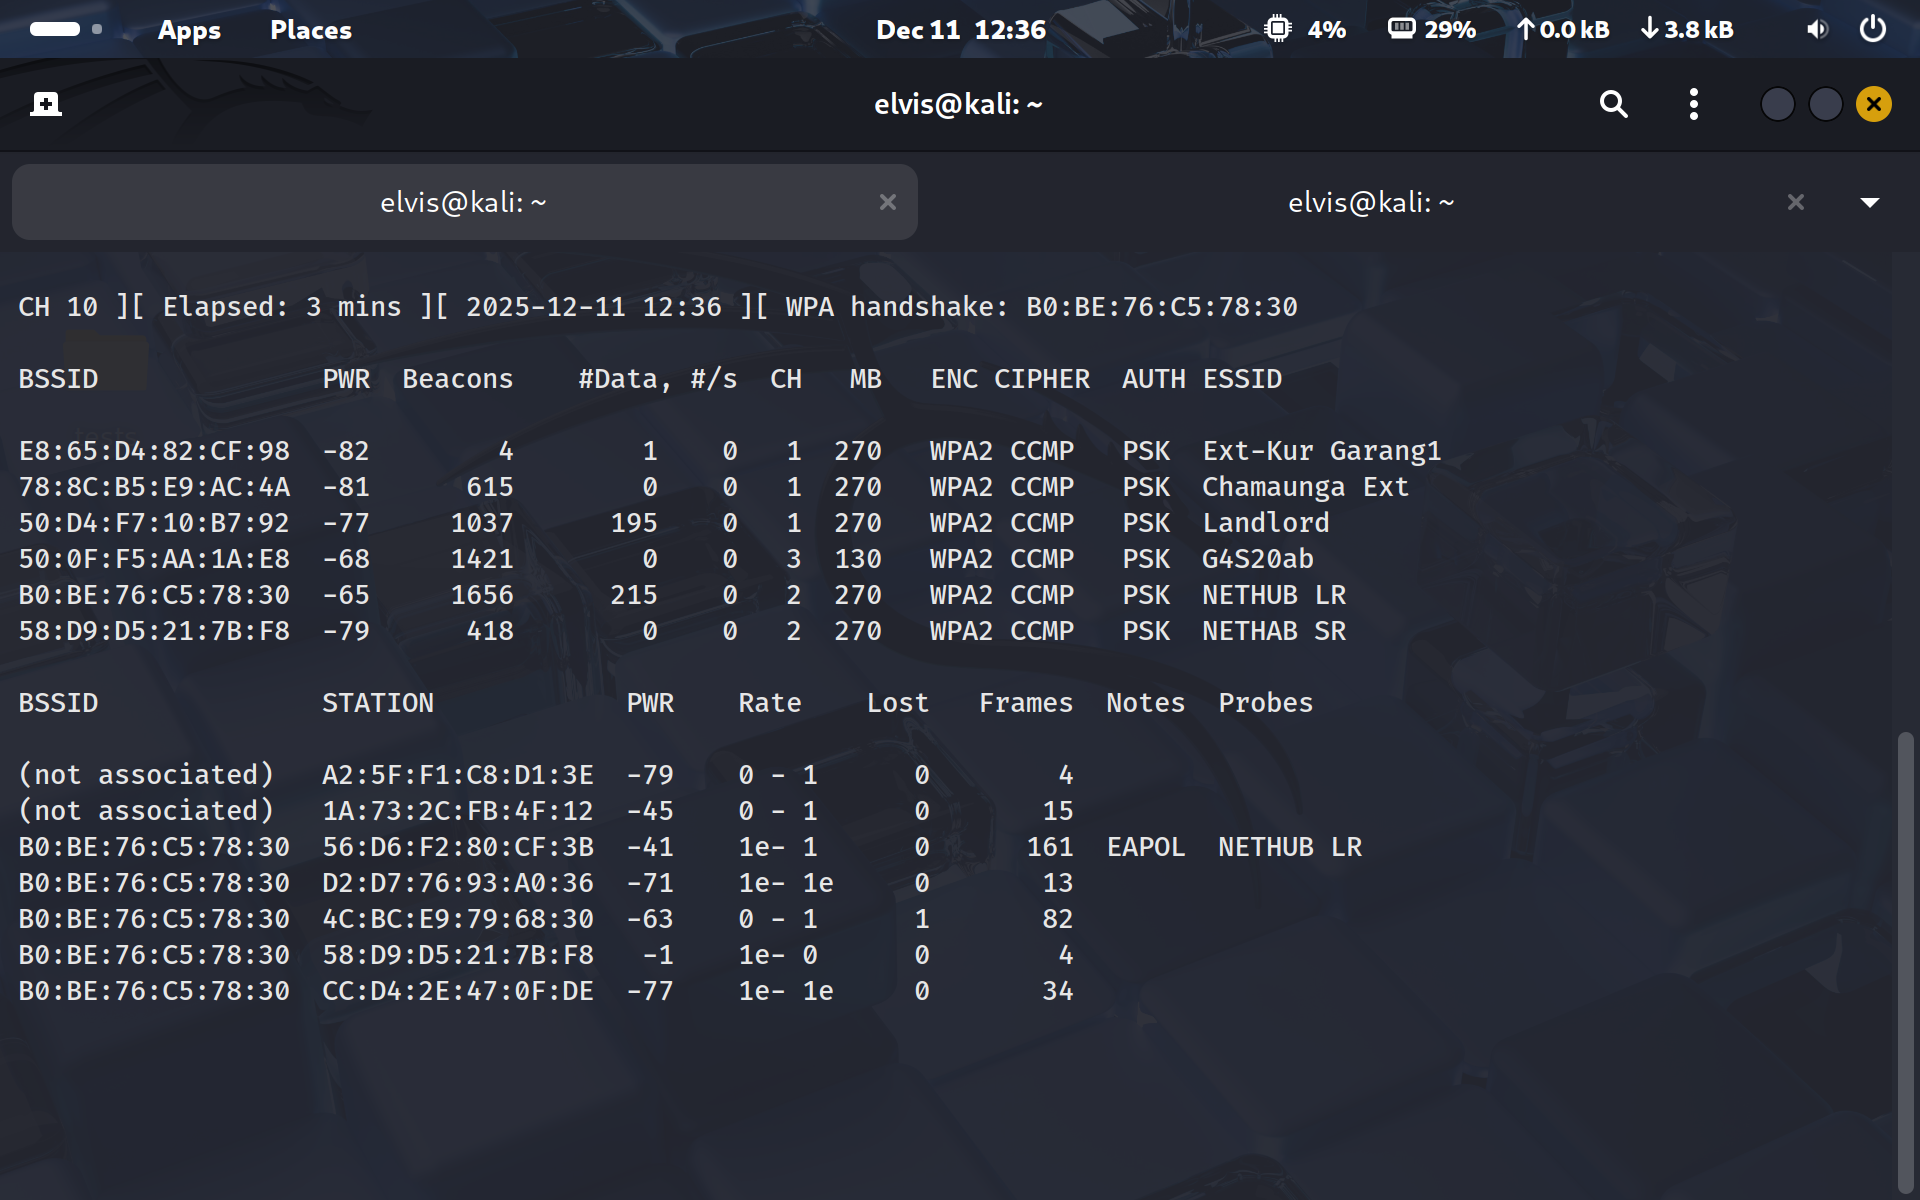 04 / 12
Network Security · 16 evidence images
Completed nine controlled wireless-security labs spanning discovery, WPA/WPA2 handshake capture, password auditing, rogue access points, WPS testing, MITM analysis, and automated assessment.
View detailed case study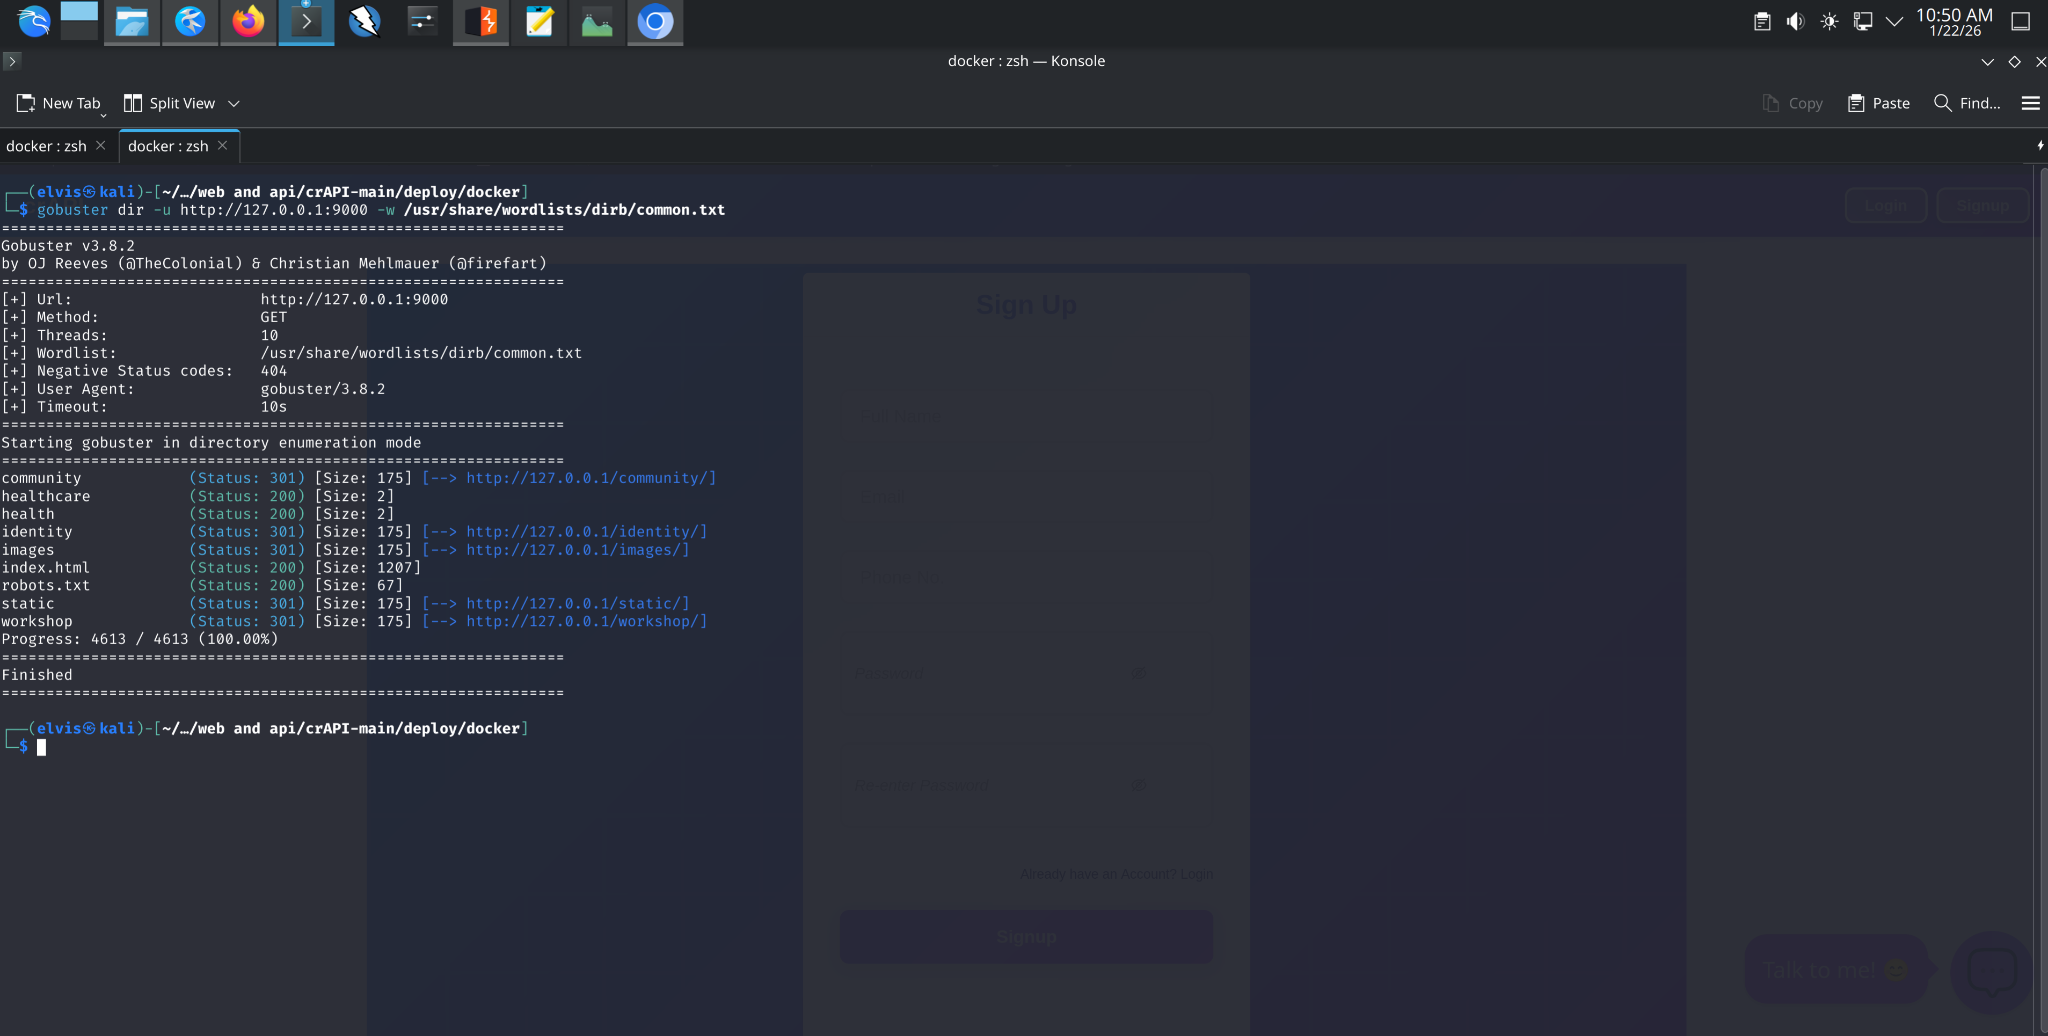 05 / 12
Web & Mobile Application Security · 20 evidence images
Executed a structured security assessment against a local OWASP crAPI deployment and translated technical proof into ten prioritized, business-readable findings.
View detailed case study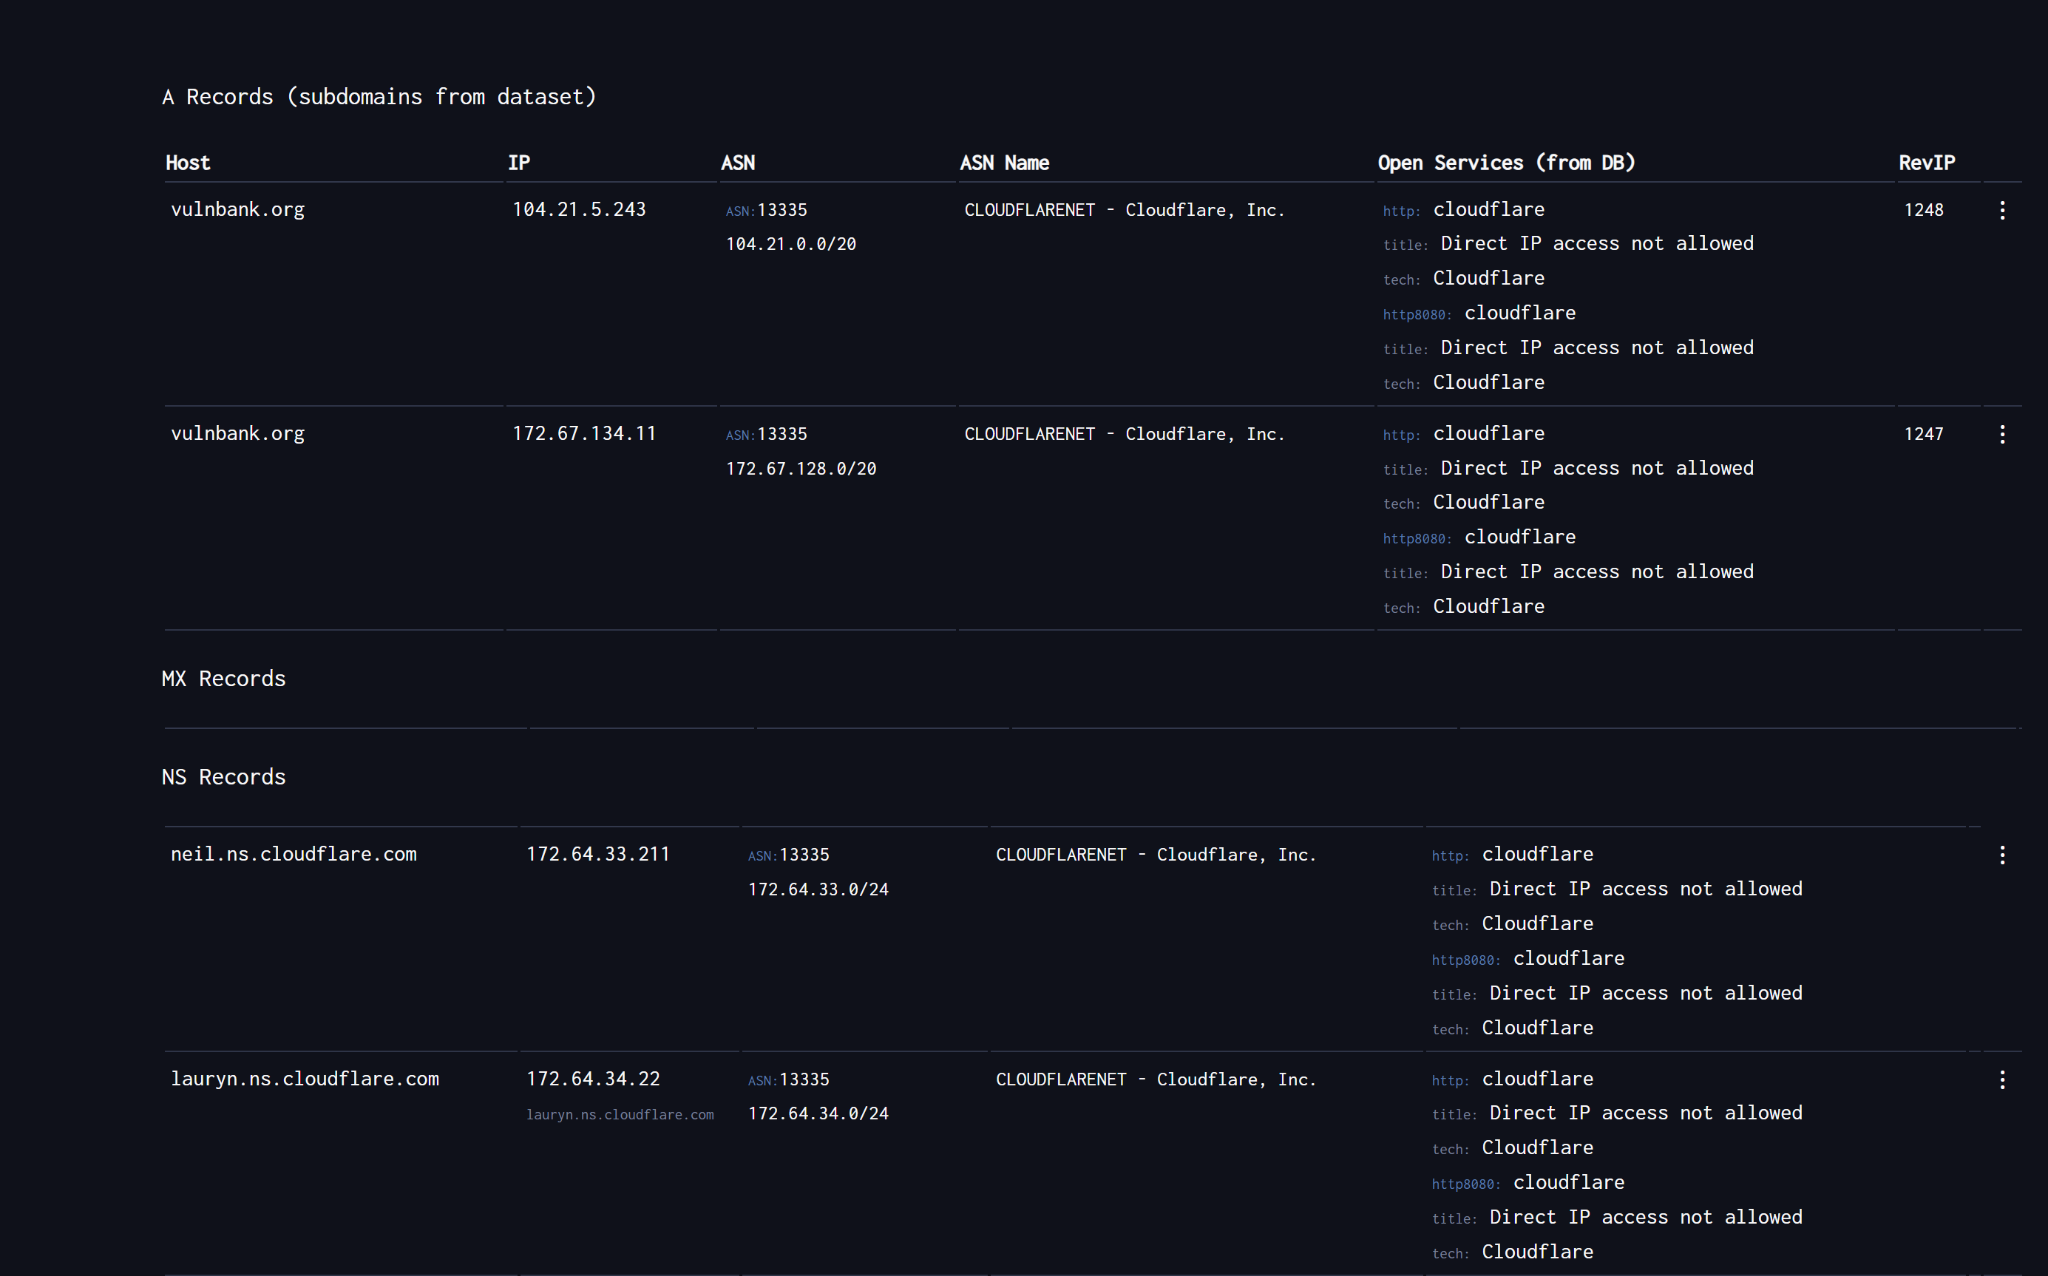 06 / 12
Web & Mobile Application Security · 23 evidence images
Assessed a banking training environment across web, API, and Android surfaces, documenting fifteen security issues with ordered proof and remediation guidance.
View detailed case study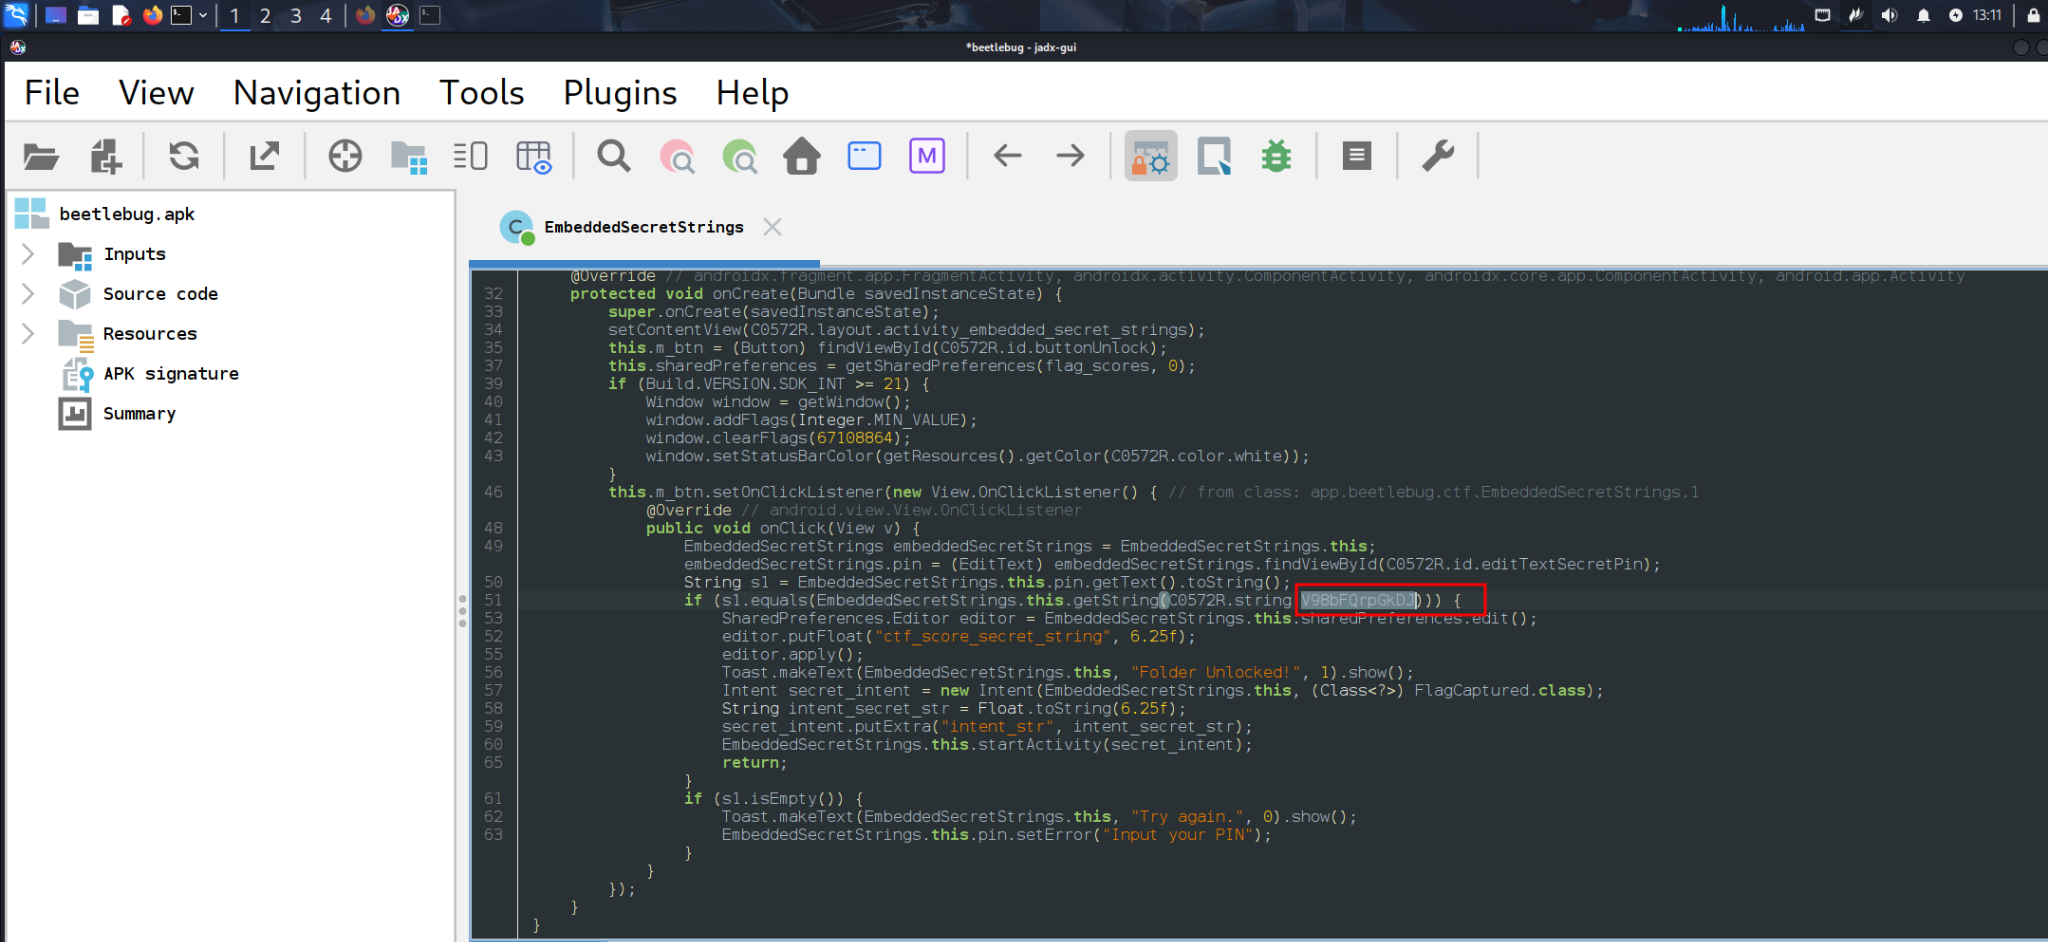 07 / 12
Web & Mobile Application Security · 18 evidence images
Performed a controlled Android application assessment using static analysis, ADB-driven dynamic testing, storage inspection, and backend validation to identify eight security weaknesses.
View detailed case study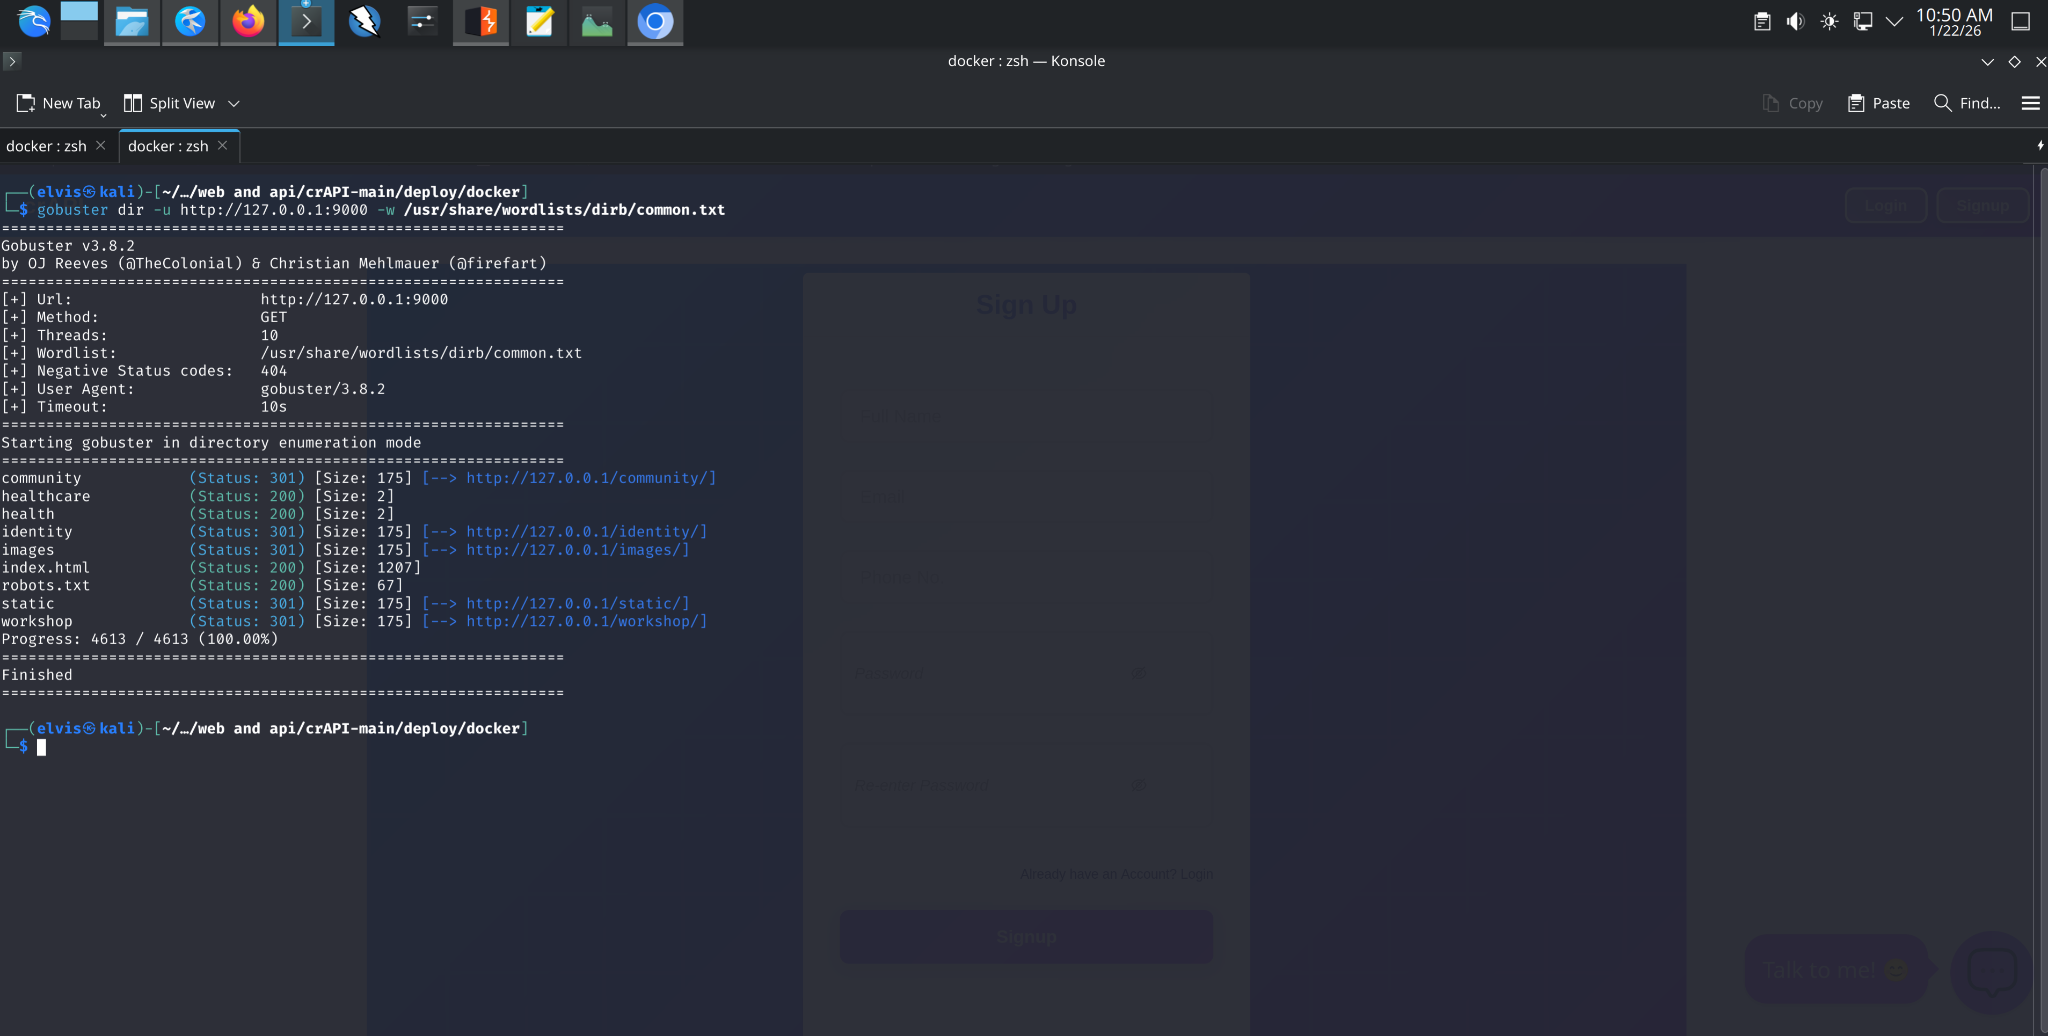 08 / 12
Web & Mobile Application Security · 20 evidence images
Validated OWASP-aligned weaknesses in a local crAPI environment, preserving request/response evidence across authorization, authentication, rate limiting, injection, and security configuration.
View detailed case study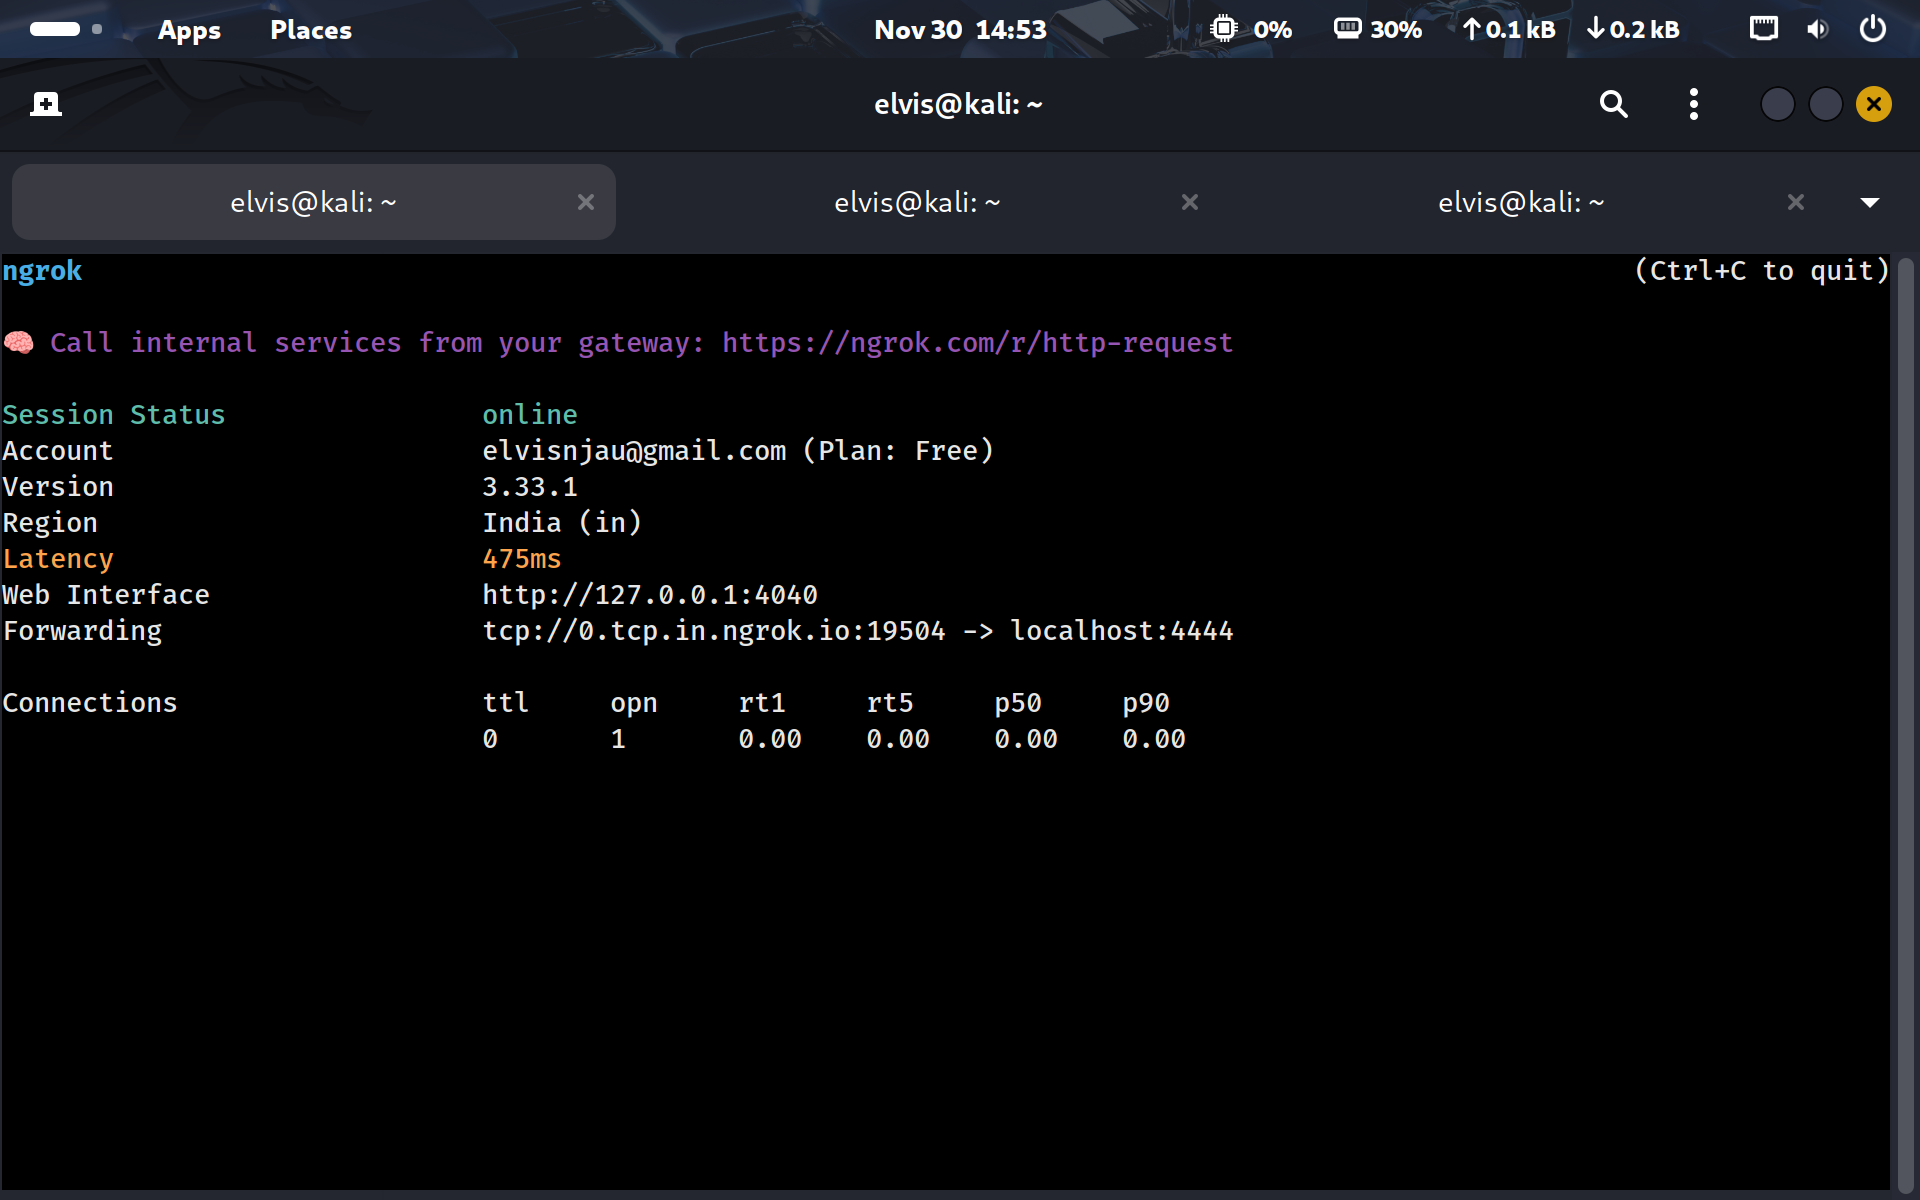 09 / 12
Endpoint Security · 5 evidence images
Completed a controlled four-stage Windows exploitation exercise using a tunnel, a generated reverse TCP payload, a Metasploit handler, and a verified remote shell.
View detailed case study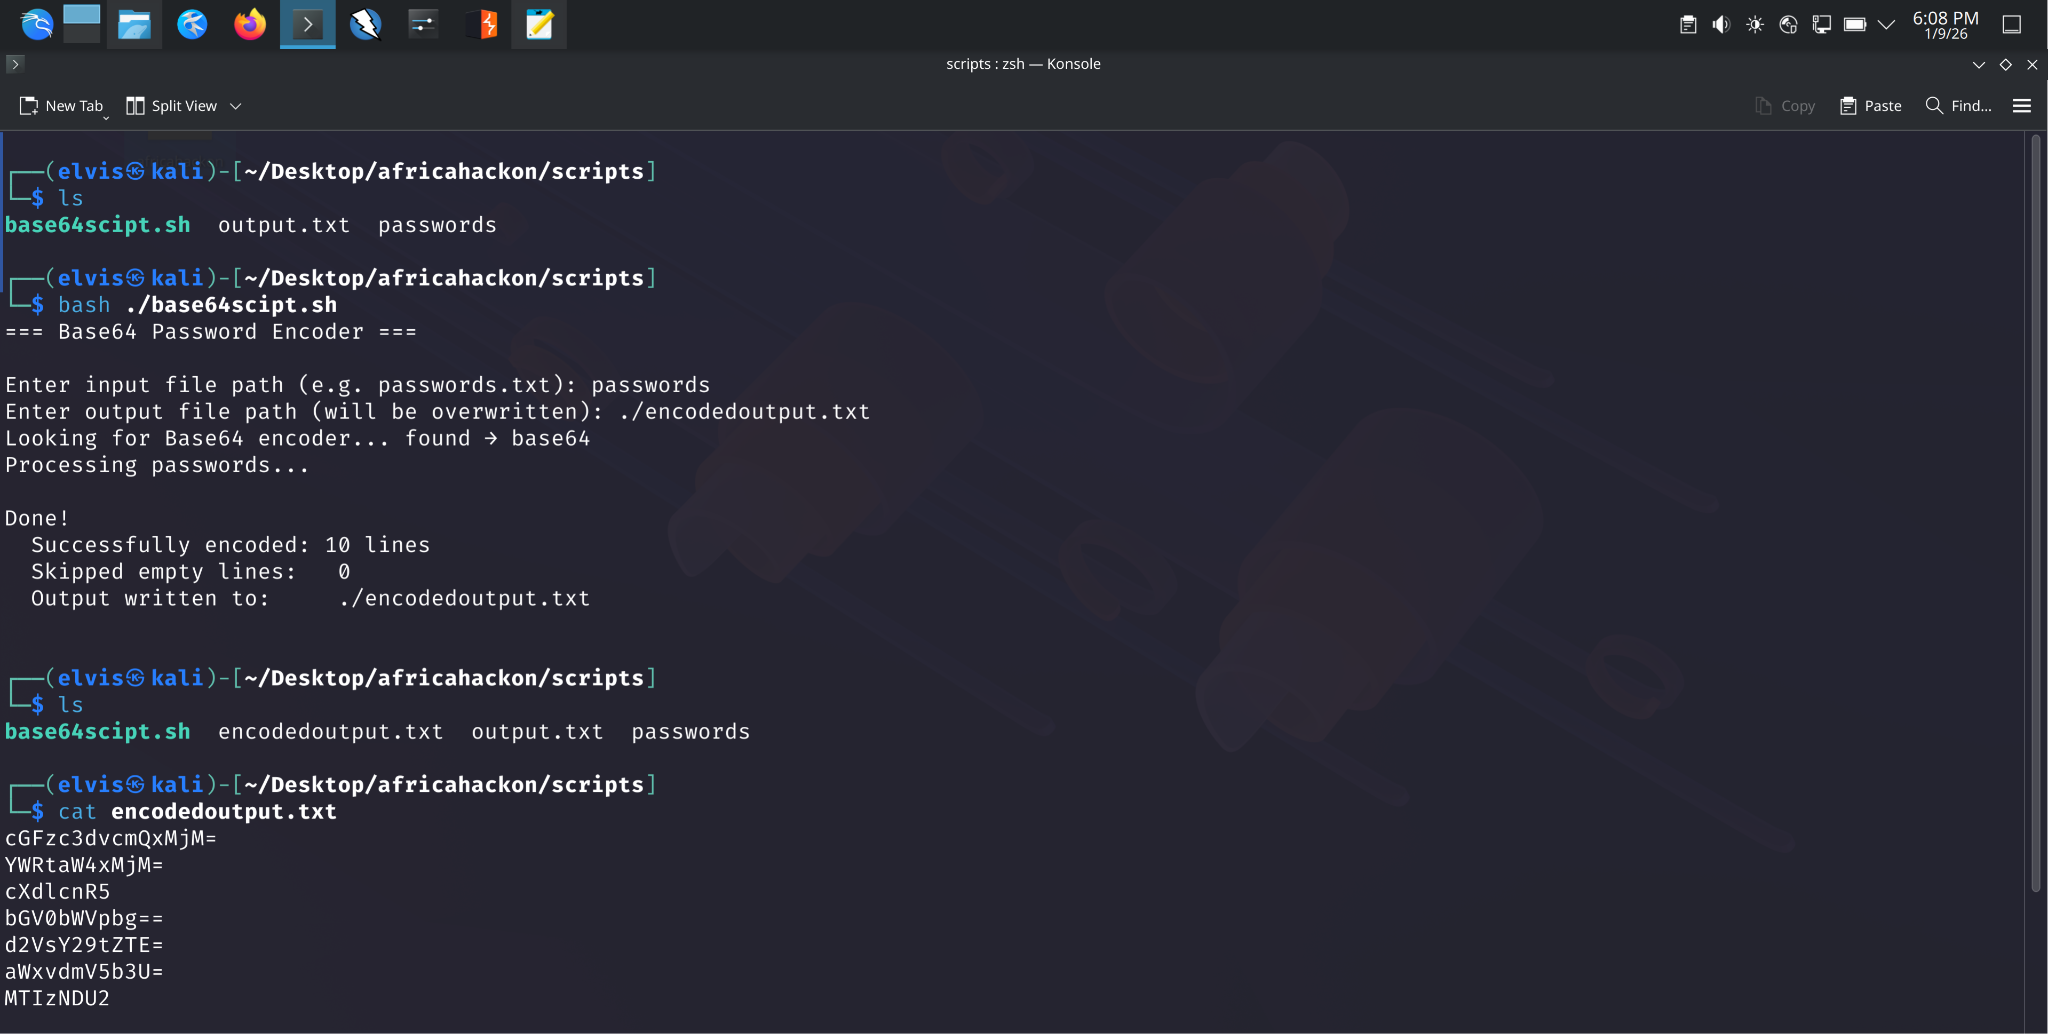 10 / 12
Scripting · 2 evidence images
Built and tested a portable Bash workflow that reads password entries, skips blank lines, selects a working Base64 implementation, and writes ordered results with explicit failure handling.
View detailed case study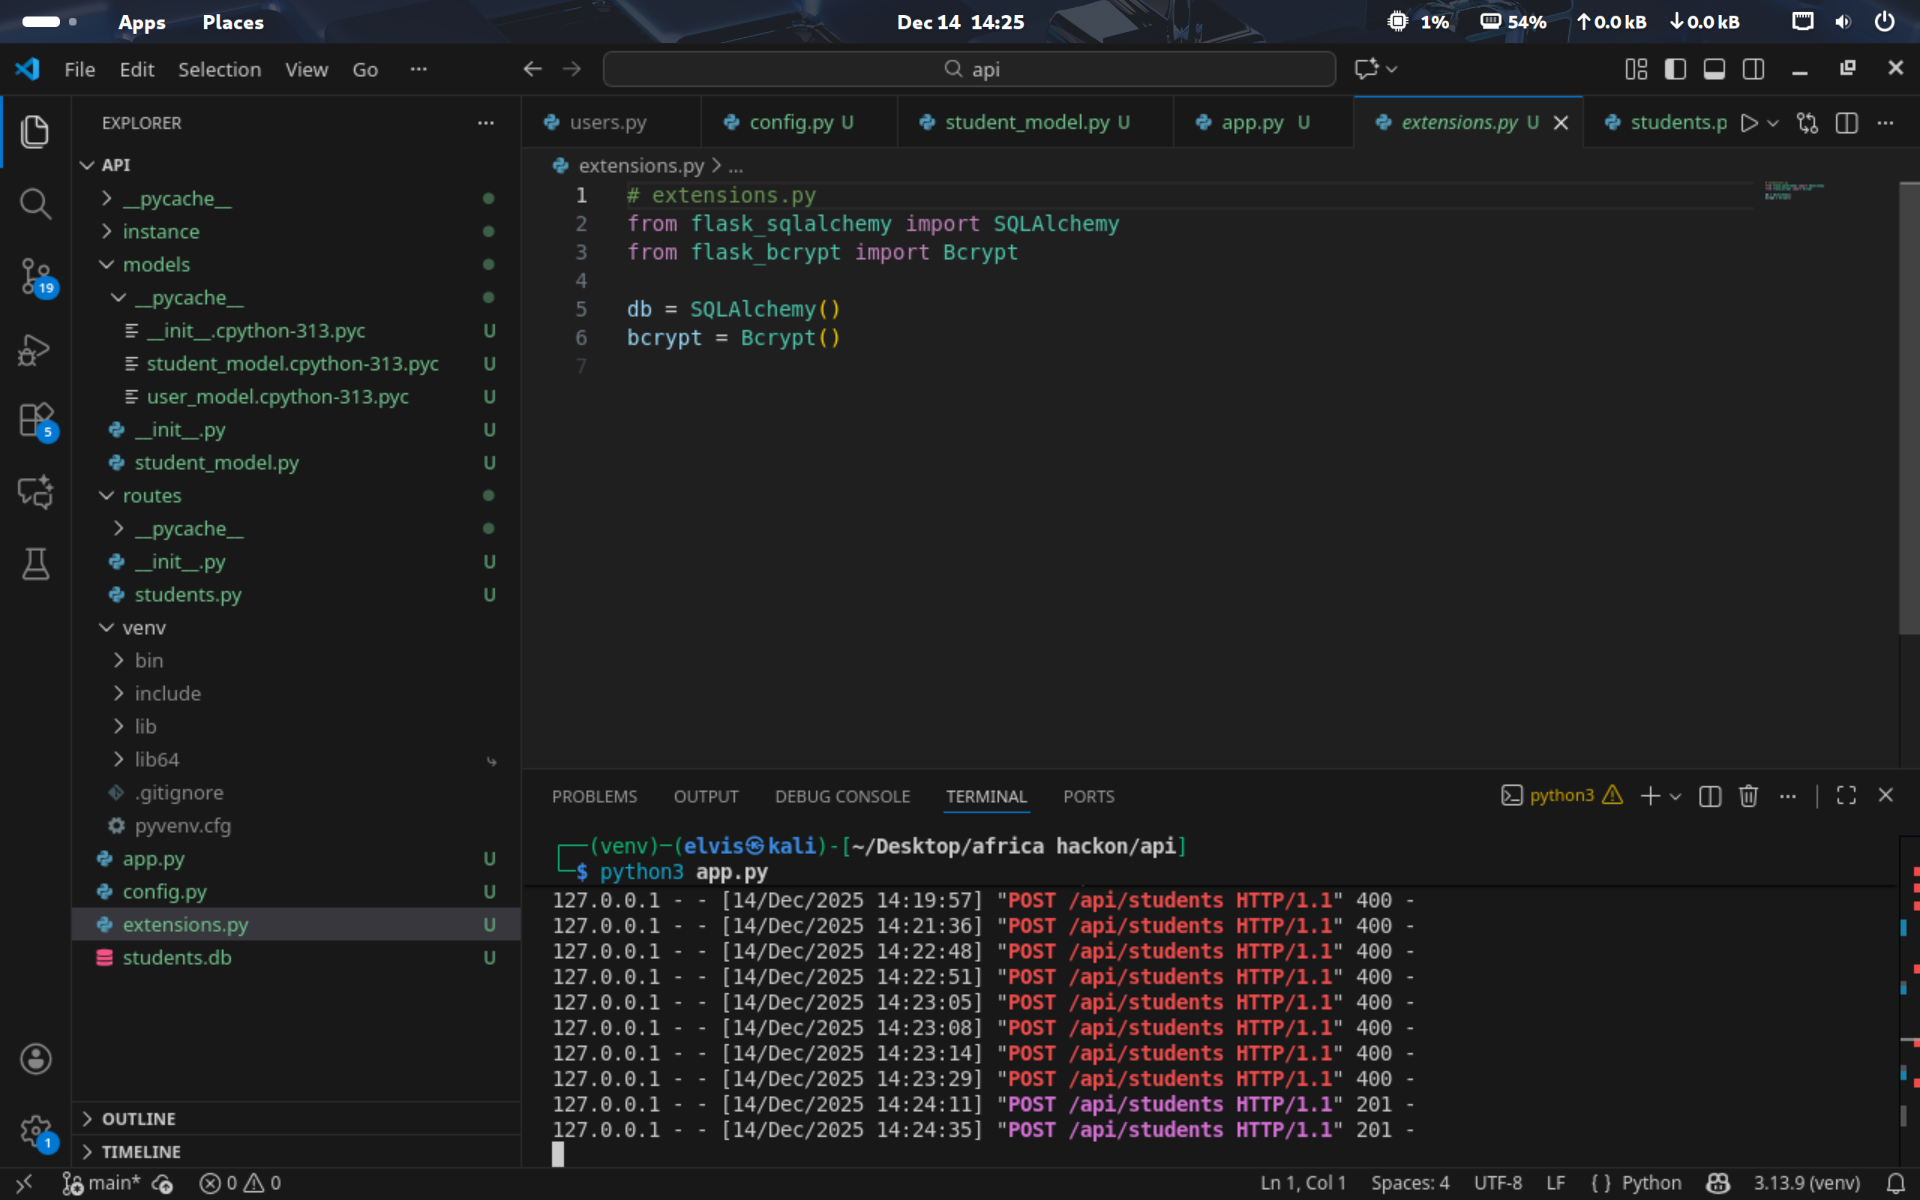 11 / 12
Engineering · 8 evidence images
Implemented and tested a Flask API that connects to a MySQL student-records database and supports create, read, update, and delete operations.
View detailed case study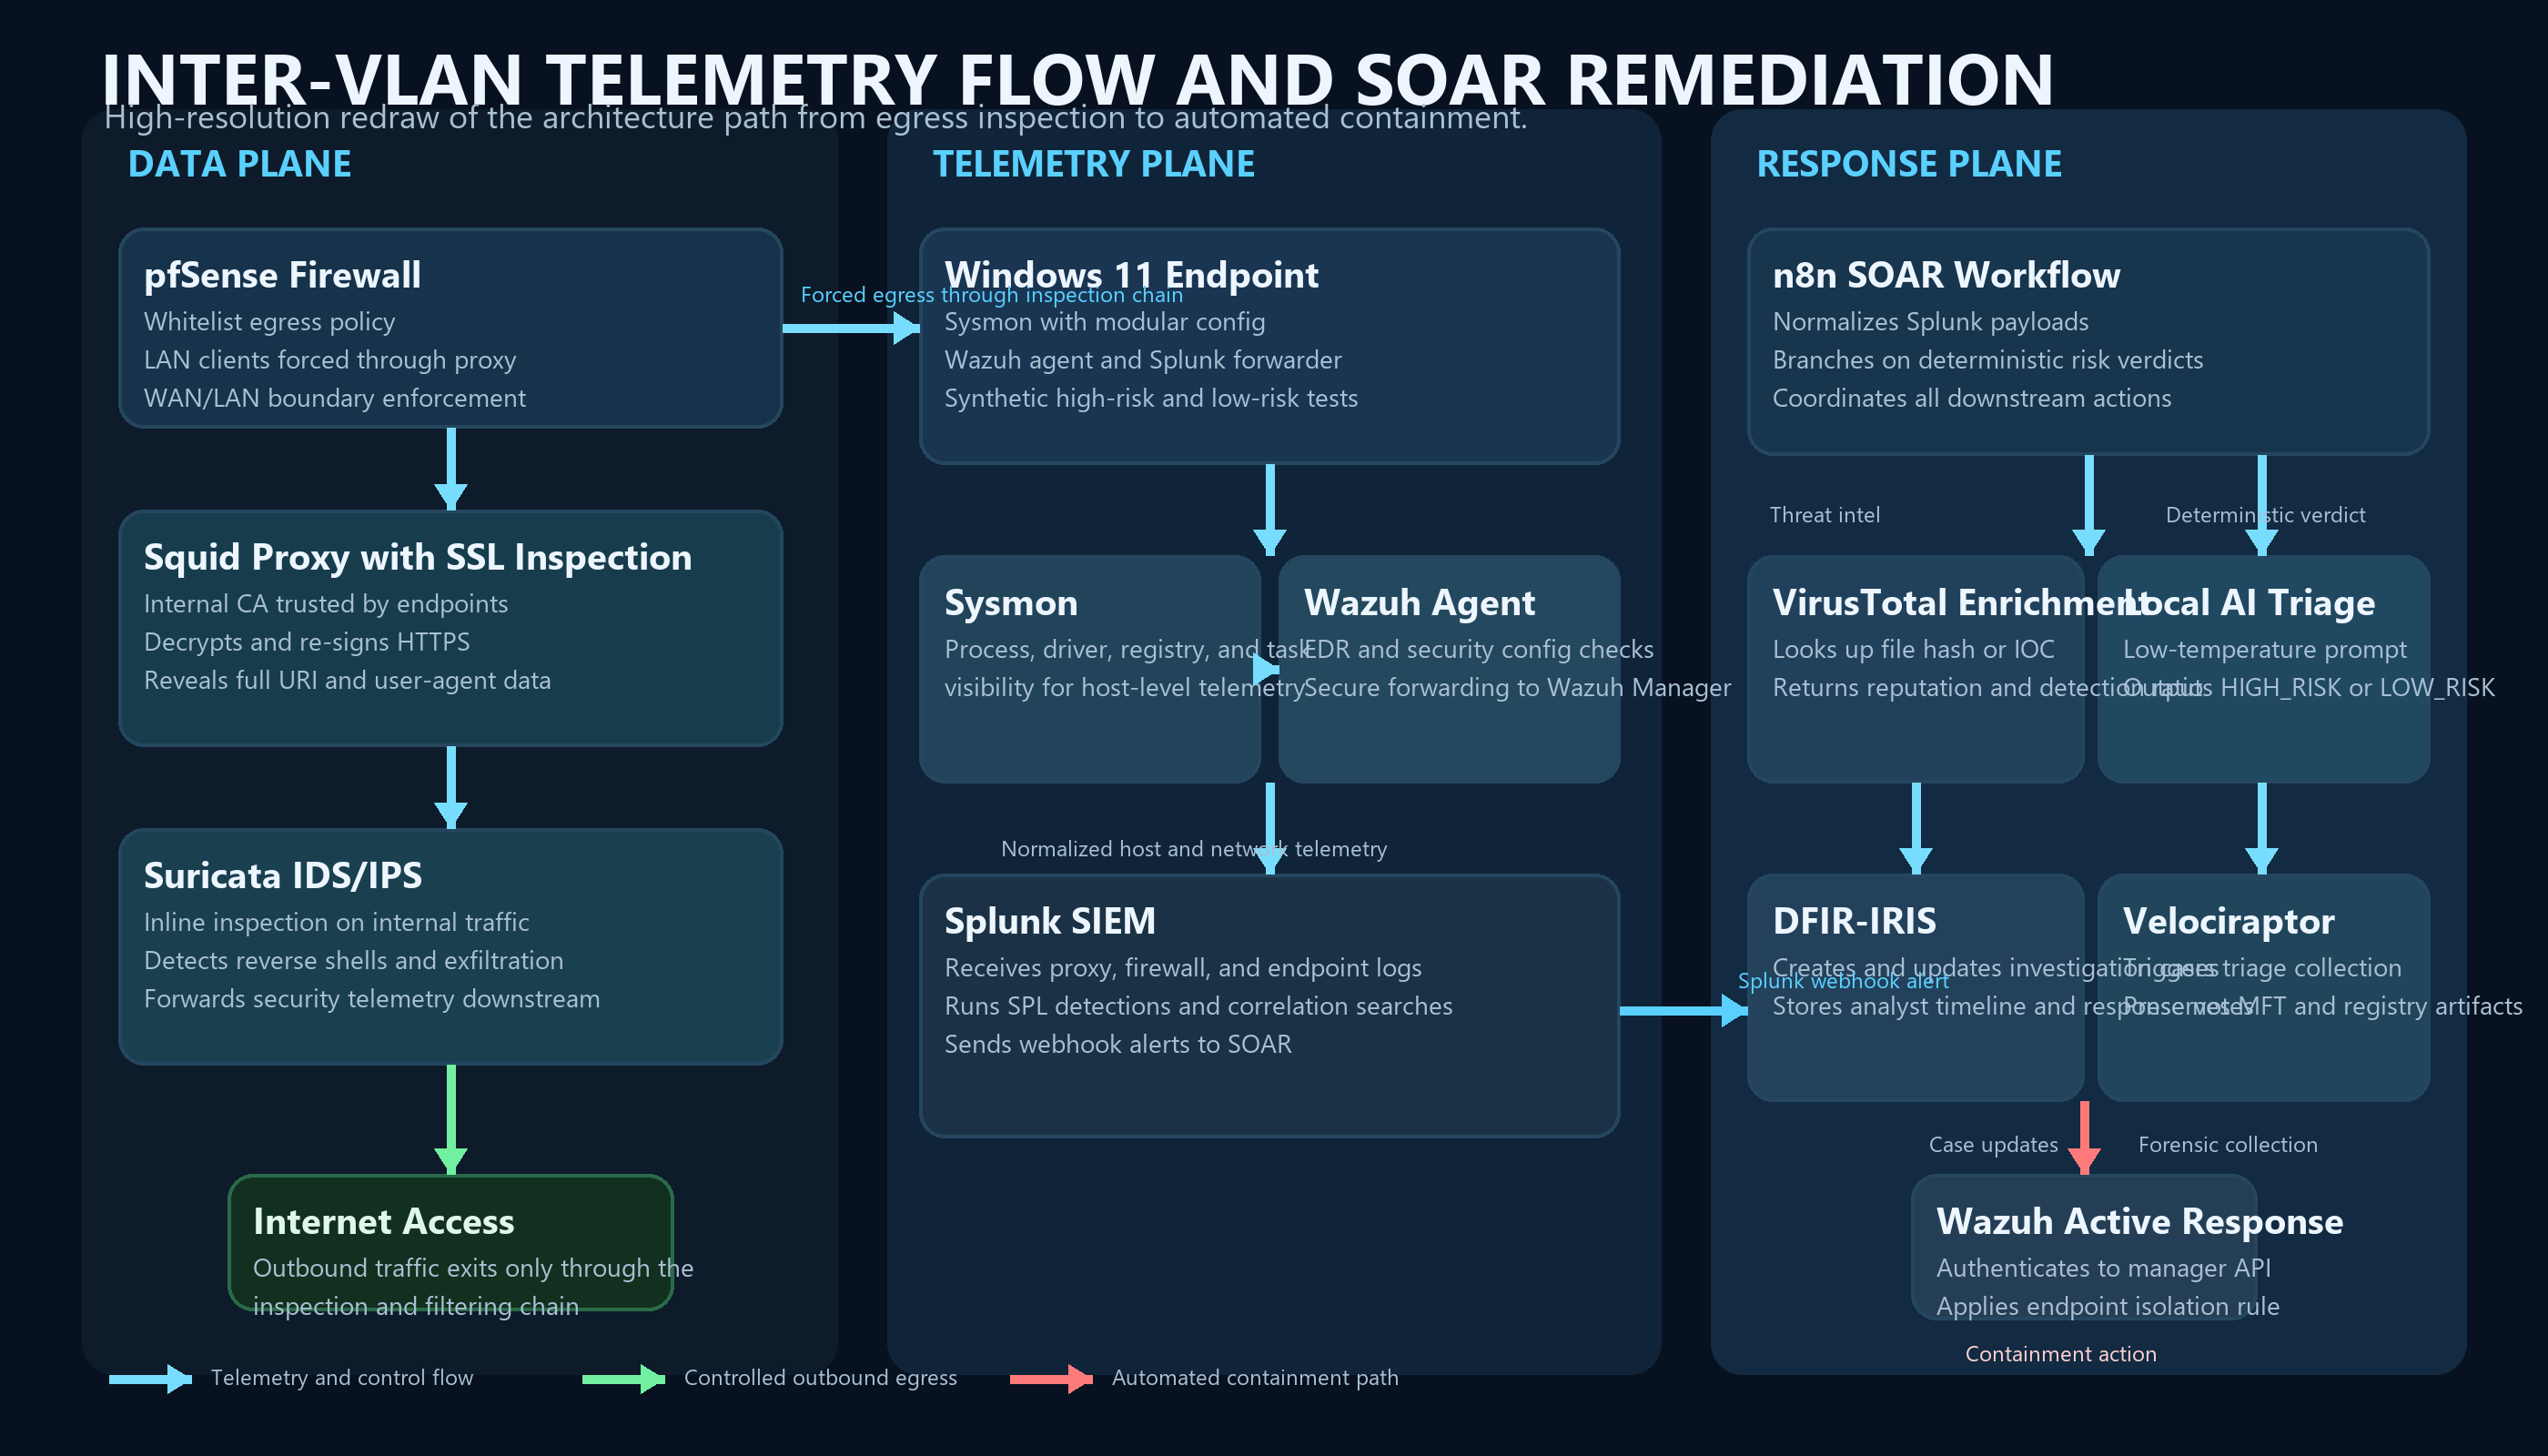 12 / 12
Detection Engineering · 14 evidence images
Built and validated an end-to-end SOC detection and response pipeline: Splunk correlation alerts trigger an n8n SOAR workflow that enriches indicators with VirusTotal v3 and asks a local LLM (`qwen/qwen3.5-9b`, temperature 0.1) for a deterministic HIGH_RISK or LOW_RISK verdict. Each alert opens a DFIR-IRIS case; high-risk verdicts automatically trigger a Velociraptor `Windows.Triage.Collection` and Wazuh Active Response host isolation, while low-risk alerts are documented and closed. The full path was validated with synthetic high-risk and low-risk scenarios, without live malware or real IOC traffic.
View detailed case studyProfessional foundation
Self-directed, home SOC lab
Mexil Tech Consultancy Limited
Kendas Hotels
Kendas Hotels
Continuous learning
Security Blue Team
Verify credentialTryHackMe
Verify credentialAfricaHackon Academy
Verify credentialAfricaHackon Academy
Verify credentialJomo Kenyatta University of Agriculture and Technology (JKUAT)
What I'm looking for
I am seeking a SOC Analyst (L2) or Detection Engineer role where I can investigate alerts end to end, build and tune detections across endpoint and network telemetry, and automate response playbooks.
Let's connect
Nairobi, Kenya · Open to remote and on-site SOC Analyst (L2) and Detection Engineer roles